Corporate Governance
Composition of the Board of Directors/ Members of the Board of Directors
The SCSB’s Board of Directors functions in accordance with applicable laws, the Articles of Incorporation and resolutions of the Shareholders Assembly. The Board currently consists of six directors and three independent directors who hold meetings on a quarterly basis. Each director serves as the director for 15 years on average. In addition, 3 Managing Directors will be elected from the Board of Directors, and 1 of whom will be an independent director. Lastly, the managing directors’ meetings are set to be held on a monthly basis. Record date: 12/31/2024
Performance Target Indicators and Weights for Senior Executives
| Indicator and weight | Description of indicator | |
|---|---|---|
| Work objectives 80% | Financial and operating performance |
|
| Implementation and progress of annual ESG goals (at least 5%) |
|
|
| Personal training and career development |
|
|
| Internal audits & controls |
|
|
| Leadership competency 20% |
|
|
President and Senior Executive Vice President Short-Term ESG-related KPIs
| Corresponding Sustainability Topic(*Annual Material Topic) | 2025 Work Goals | Weights (%) | |
|---|---|---|---|
| Sustainable Finance* | Customer Aspect | Amounts of green lending and green investment increased by 15% compared with the previous year. | 2 |
| Customer Relationship and Fair Customer Treatment | Customer Aspect | Rank among the top 25% for FSC’s Treating Customers Fairly Principles Assessment Program | 2 |
| Digital Finance and Service Innovation* | Logistic Aspect | Completed no fewer than five artificial intelligence (AI) application scenarios and increased the proportion of digital financial transactions to at least 85%. | 3 |
| Climate Strategy and Management*
Green Operations and Net Zero Actions* |
Finance Aspect | Completed the “Climate and Nature Environment Management Report” and the “Sustainability Report” on schedule and disclosed them on the SCSB’s official website; green electricity usage accounted for 12% of the SCSB’s total electricity consumption. | 5 |
| Logistic Aspect | Completed greenhouse gas inventory, verification, and disclosure as scheduled in accordance with the regulatory authorities’ timeline, and advanced the adoption of the IFRS S1 and S2 Sustainability Disclosure Standards. | 2 | |
| Logistic Aspect | Implemented the carbon reduction pathway as planned in accordance with the Science-Based Targets (SBTs) submitted by SCSB. | 2 | |
| Logistic Aspect | Energy and resource reduction targets: – Greenhouse gas emissions intensity per unit of revenue (entity’s net income) for Scope 1 and Scope 2 decreased by 3% compared with 2020. – Absolute greenhouse gas emissions for Scope 1 and Scope 2 decreased by 4% compared with 2020. | 2 | |
| Occupational Health and Safety*
Employee Training and Career Development |
Learning and Growth Aspect | In line with strategic priorities and operational objectives, the SCSB focuses on cultivating key talent required over the next three to five years, including 30 professionals each in international finance, digital finance, sustainable finance, information technology, artificial intelligence (AI), and business-line marketing. | 2 |
| Learning and Growth Aspect | To foster a healthy workplace environment, the SCSB completed employee engagement and satisfaction surveys to enhance and optimize the overall employee experience. | 2 | |
| Legal Compliance*, Information security*, Data Privacy and Protection* | Internal Control Aspect | No major anti-money laundering deficiencies or information security incidents occurred throughout the year | 4 |
| The total proportion of short-term ESG-related KPIs | 26 | ||
Members of the Board of Directors
| Name | Title | External independence (Note 2) |
Nationality | Gender | Age | Professional qualifications and experience (Note 3) |
Term | Board of Directors Attendance Rate (%) |
|---|---|---|---|---|---|---|---|---|
| Lee Ching-Yen Stephen | Chairman, Managing Director | Non-executive director Independent director | Singapore | Male | >50 | Finance, industrial, non-essential consumer goods | 47 | 100% |
| Yung Con-Sing John (Representative: Magnetic Holdings Limited) | Vice Chairman, Managing Director | Hong Kong | Male | >50 | Finance, non-essential consumer goods, real estate | 23 | 100% | |
| Chen Mu-Tsai | Independent Director, Managing Director | Republic of China (Taiwan) | Male | >50 | Finance | 8 | 100% | |
| Yung Chu-Kuen | Director | Republic of China (Taiwan) | Male | >50 | Finance, non-essential consumer goods | 35 | 100% | |
| Chiou Yi-Jen | Director | Republic of China (Taiwan) | Male | >50 | Finance | 20 | 100% | |
| Huang Hui-Chu(Representative: Tilsbury Investments Inc.) | Director | Republic of China (Taiwan) | Female | >50 | Non-essential consumer goods, information technology | 2 | 100% | |
| Kuo Ching-Yi | Director | Executive Director | Republic of China (Taiwan) | Male | >50 | Finance | 2 | 100% |
| Tseng Kuo-Lieh | Independent Director | Non-executive director Independent director | Republic of China (Taiwan) | Male | >50 | Finance, real estate | 5 | 100% |
| Fung Yen-Ling | Independent Director | Non-executive director Independent director | Republic of China (Taiwan) | Female | >50 | Finance, information Technology, non-essential consumer goods, healthcare | 2 | 100% |
Note 1: A director is evaluated as the independent director by complying with external independence based on the standard below. The director must be a non-executive director and he must meet at least four indices out of the nine indices below and must meet at least two indices out of the first three indices:
- The director must not have been employed by the company in an executive capacity within the last year.
- The director must not accept or have a “Family Member who accepts any payments from the company or any parent or subsidiary of the company in excess of $60,000 during the current fiscal year,” other than those permitted by SEC Rule 4200 Definitions
- The director must not be a “Family Member of an individual who is employed by the company or by any parent or subsidiary of the company as an executive officer.”
- The director must not be (and must not be affiliated with a company that is) an adviser or consultant to the company or a member of the company’s senior management.
- The director must not be affiliated with a significant customer or supplier of the company.
- The director must have no personal services contract(s) with the company and cannot be a member of the company’s senior management.
- The director must not be affiliated with a not-for-profit entity that receives significant contributions from the company.
- The director must not have been a partner or employee of the company’s outside auditor during the past year.
- The director must not have any other conflict of interest that the board itself determines to mean they cannot be considered independent.
NOTE 2: According to Article 4 of the Regulations Governing Appointment of Independent Directors and Compliance Matters for Public Companies, our independent director must not concurrently serve as an independent director of more than three public companies.
Note 3: Evaluate the director's experience in the industry based on GICS Level 1.
Note 4: According to the SCSB’s “Articles of Incorporation”, the proportion of each director attending the board meeting in person should reach more than 80% every year. Moreover, it’s required to seek shareholders’ approval before making any changes to the bylaws.
NOTE 5: Based on “ Company Act of Taiwan”, directors are legally obligated to fulfill their duties of loyalty and the duty of care of a good manager. Articles 193 and 200 of the Company Act specify that if a director violates the law or the company's Articles of Incorporation, resulting in damages to the company, they shall be liable for damages to the company. This responsibility is a mandatory legal regulation and cannot be restricted or exempted through internal company rules or Articles of Incorporation. The SCSB does not have any clauses or agreements that limit directors' responsibilities, so in the corporate governance structure, directors' responsibilities are not limited.
President and Executive Committee members’ multiple of base salary
In December 2025, the President of the SCSB Kuo, Ching-Yi possessed 1,142,135 shares with 5.92 times of his base salary while the Senior Executive Vice President Chang, Wen-Chen held 700,000 shares with 6.53 times of his base salary, and the First Executive Vice President Huang, Ping-Hua held 788,251 shares with 7.36 times of his base salary.
Note: The calculation of multiple of base salary (number of shares held by a person* share price at the end of FY25, namely NT$ 40.6)/ base salary of a person
President-to-Employee Pay Ratio
The ratio between the total annual compensation of the President of the SCSB and its median and mean employee compensation was 12.04 and 10.86 in 2025 respectively
Anti-money Laundering
In order to tighten requirements concerning anti-money laundering and counter-terrorism financing, internal control, and compliance in banks, the SCSB has established a group anti-money laundering policy and the relevant procedure. A dedicated Anti-Money Laundering and Counter-Terrorism Financing Center has been established under the Compliance Department with a responsible officer, and an inter-departmental Anti-Money Laundering and Counter-Terrorism Financing Committee has also been established. Supervisory officers for anti-money laundering and counter-terrorism financing have been appointed to all of our business units to build a top-down hierarchical management system. The external independent verification unit has been authorized every year to conduct the Anti-Money Laundering and Counter-Terrorism Financing Program Review.
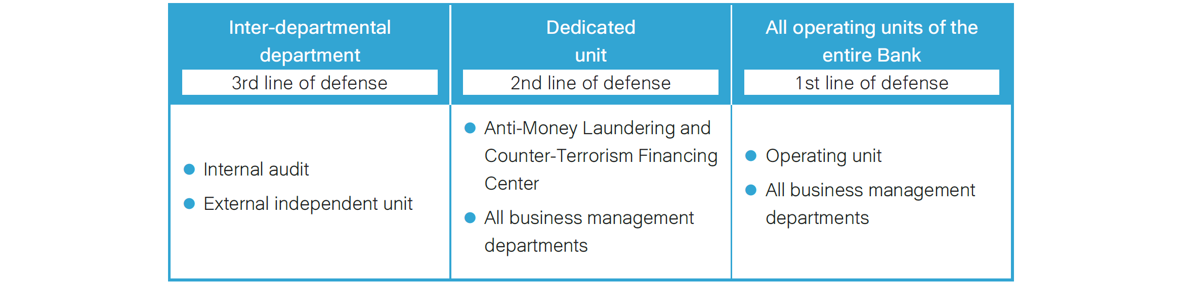
The SCSB performs three lines of defense for anti-money laundering and counter-terrorism financing. For the first line, the business unit conducts customer and trade reviews and self-evaluation. (The business exclusive to the business unit is conducted by the business unit.) For the second line, the Anti-Money Laundering and Counter-Terrorism Financing Center (dedicated unit) and all business management departments carry out supervision. In addition to operation planning for anti-money laundering and counter-terrorism financing, the Center and all of these business departments execute activity spot checks and assessments for business units. (The KPI item for the business unit and its compliance manager includes tasks for anti-money laundering and counter-terrorism financing.) For the third line, the internal audit unit and an external independent unit conduct third-party verification at least once a year.
The head of the Anti-Money Laundering and Counter-Terrorism Financing Center and managers of all branches discuss on anti-money laundering and counter-terrorism financing issues at quarterly compliance meeting. If any business unit has any concerns about the implementation of anti-money laundering and counter-terrorism financing, it may report its concern to the Anti-Money Laundering and Counter-Terrorism Financing Center via internal consulting form. Through the establishment of an internal counseling system, the SCSB can reinforce the effectiveness of three lines of defense and communication between lines of defense.
In addition, to enhance effectiveness and efficiency of anti-money laundering and counter-terrorism financing education training, the SCSB gradually reinforces application of RegTech. The SCSB uses these technologies for customer due diligence (CDD), regular review, transaction monitoring, and characterization threshold calibration to increase efficiency and reduce labor burden. For example:
- Developing and utilizing API technology to automatically retrieve ownership structures of corporate customers with complex shareholding structures from official government websites and to calculate ultimate individual shareholdings within the system for the identification of ultimate beneficial owners (UBOs). APIs are also used to integrate information from commercial registration websites, including company operating status (active, suspended, closed, dissolved, or under liquidation), multiple companies registered at the same address, and individuals serving as responsible persons for multiple companies.
- The SCSB participates in the development of a project for optimization of the CTP system of Taiwan Depository & Clearing Corporation. The multiple layer shareholding information is added to enhance the utilization of domestic shareholding information via the real-time/batch download function of Application Programming Interface (API). This effectively assists in identification of beneficial ownership in the complex shareholding structure for anti-money laundering.
- Establishing a Hawk Eye early warning model to detect suspicious and potentially unlawful transactions, enabling timely fraud prevention and interdiction.
- Strengthening preventive fraud controls, such as enhancing review procedures for applications to adjust transfer limits for automated services, and reinforcing controls over higher-risk accounts, including accounts of foreign migrant workers and long-inactive accounts.
- Developing an “AML Typology Parameter Analysis System” for parameter calibration and optimization.
Anti-money Laundering and Counter-terrorism Financing Education Training
In order to continue to help employees learn more about anti-money laundering and counter-terrorism financing, the SCSB held 102 seminars with a total of 388 hours for anti-money laundering and counter-terrorism financing in 2025. To build a culture that emphasizes anti-money laundering and counter-terrorism financing, the SCSB offers subsidies to help staff become the CAMS international anti-money laundering specialists or take the exams organized by domestic institutions recognized by the Financial Supervisory Commission for Anti-Money Laundering and Counter-Terrorism Financing Specialists. Via E-LEARNING and morning meetings, education training for anti-money laundering and counter-terrorism financing is provided by sharing ideas on a topic. A total of 16 sessions were held during morning meetings in 2025. (A total of 165 sessions were held from May 2017 to December 2025.) All staff were required to attend the seminars.
In addition, the SCSB actively encourages employees to acquire professional licenses for anti-money laundering and counter-terrorism financing and pass the relevant exam. The number of staff with professional licenses for anti-money laundering and counter-terrorism financing and qualifications for passing certain exams in 2025:
| Item | The number of staff |
|---|---|
| Certified Anti-Money Laundering Specialist (CAMS) | 229 |
| Professional Exam for Anti-Money Laundering and Countering Terrorism Financing Specialist | 1,227 |
Donation to the SCSB Associated with Political/Policy Impact
| Unit: NT$ | ||||
|---|---|---|---|---|
|
Year
Donation and expenditure |
2022 | 2023 | 2024 | 2025 |
| Policy lobbyist, lobbying organization and lobbying interest group | 0 | 0 | 0 | 0 |
| Political organizations and candidates | 0 | 0 | 0 | 0 |
| Industrial trade associations and think tank groups affecting campaign or legislation | 0 | 0 | 0 | 0 |
| Others, such as expenditure for election issue and referendum | 0 | 0 | 0 | 0 |
| Total | 0 | 0 | 0 | 0 |
| Scope | 100% | 100% | 100% | 100% |
Ethical Management
Zero tolerance policy is adopted for violation against internal work rules such as relevant regulations, “Code of Ethical Conduct” and “Ethical Corporate Management Best-Practice Principles”. In 2025, the SCSB received a total of 17 reported cases. Among these cases, 8 fell outside the scope defined under the “Procedures for handling Whistleblowing” and were therefore referred to the responsible business units for follow‑up. In addition, 6 cases were not accepted due to failure to supplement required information, being limited to information transmission only, or requests for withdrawal. A total of 3 cases were formally accepted and processed.
Furthermore, in 2025, the following information is disclosed regarding incidents that were not discovered through whistleblowing: The SCSB was not involved in any cases associated with conflicts of interest, customer privacy information leaks, money laundering and insider trading, anti-competitive practices, antitrust and monopoly behavior, or any relevant legal disputes and penalties regarding market manipulation.In 2025, one incident related to corruption or bribery occurred. For a description of the case, please refer to Section 2.3.1 Compliance Risk Assessment Process.
Ethical Management Training and Communication
At SCSB, ethical management is the foundation of stable governance. To make sure that employees understand anti-corruption regulations, besides internal messages, unit managers and announcements to all employees, anti-corruption is also promoted at morning meetings and via the precautions in the Ethical Corporate Management Best-Practice Principles. The promotion covers all employees. As for the Board of Directors, anti-corruption is communicated via corporate governance forum. The anti-corruption trainings are designed for employees based on their job grades and business types (in which visual disabilities are accommodated with oral training sessions instead). The following is the information related to such courses organized in 2025.
| Region covered | Course target | Number of employees taking the course | No. of participants | Percentage of participants among the course target |
|---|---|---|---|---|
| Taiwan, Hong Kong, Vietnam, Singapore, China (Wuxi), Thailand, Cambodia, and Indonesia | ||||
| Non-managerial employees | 2,499 | 2,499 | 100% | |
| Managerial employees | 372 | 372 | 100% | |
| Directors | 9 | 9 | 100% |
Note: The statistics are based on employees in service at The Shanghai Commercial & Savings Bank as of the end of 2025. The President is also included in the count of managerial staff for education and training purposes.
| Worker group | Coverage (%) | Written/ Electronic signing statement (%) | Providing education training (%) |
|---|---|---|---|
| Employees | 100 | 100 | 100 |
| Contractor/Supplier/Service provider | 100 | 100 | 100 |
| Subsidiary | 100 | 100 | 100 |
Procedures Tailored to Whistleblowing
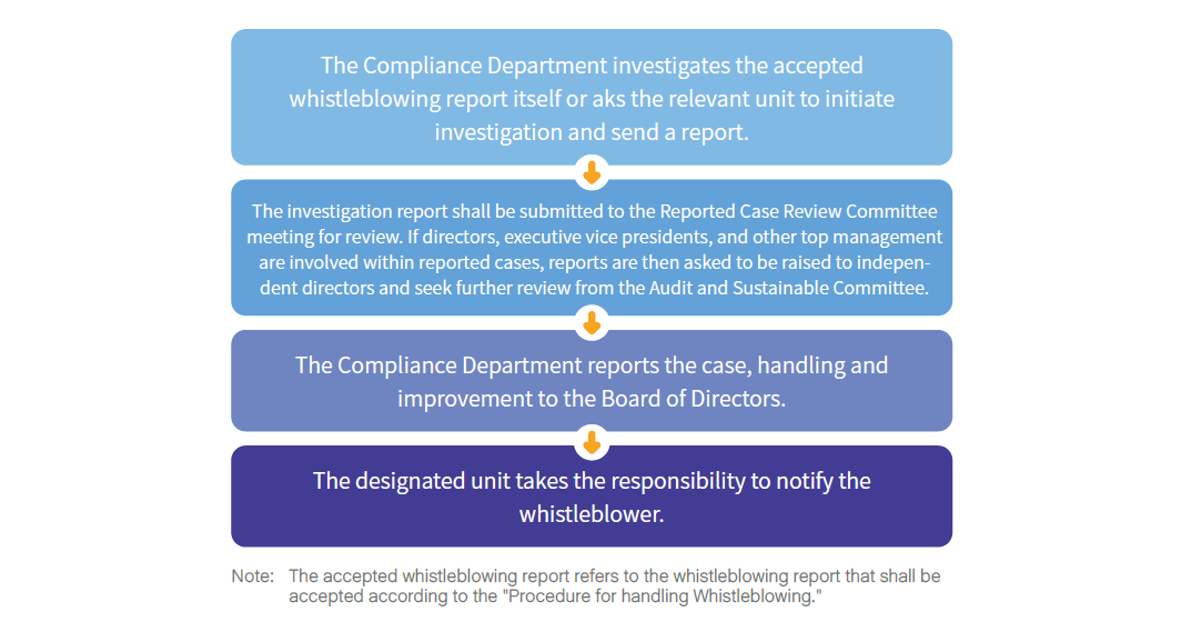
“Procedure for handling Whistleblowing” have been established to encourage employees to report cases of violations. The SCSB will do its best to protect the whistleblowers, including keeping personal information confidential and making sure that their rights and interests are not affected. The Compliance Department accepts the case and investigates the dedicated unit being reported. When receiving a case, the Compliance Department may ask the relevant unit or the Chief Auditor to appoint auditors to investigate the case. Handling of the case is described below :
Whistleblowing Processing Method and Channel
Whistleblowing mailbox:compliance@scsb.com.tw
Whistleblowing helpline: (02)6618-9952
Postal address: No. 2, Sec. 1, Minquan E. Rd., Zhongshan Dist., Taipei City. The recipient information should be stated as the Chief Compliance Officer
Details for the SCSB’s announcement: https://www.scsb.com.tw/content/about/about21.html
Risk Management
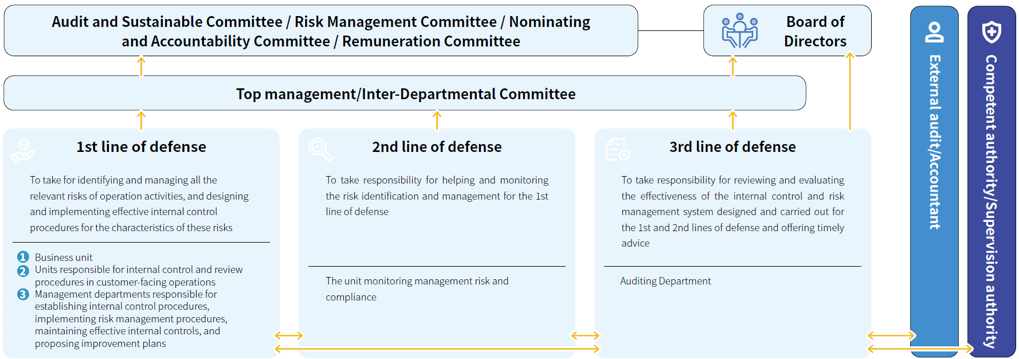
In the SCSB’s risk management organizational structure, the Board of Directors serves as the highest decision making body. Board members are required to receive at least six hours of risk related training each year, covering risk control topics such as anti money laundering, anti corruption, and information security. A Risk Management Committee has been established under the Board of Directors to oversee bank wide risk management. Under the President, the Risk Management Department is responsible for establishing a bank wide risk management framework and independently performing its duties in relation to enterprise wide risk management. Each responsible unit appoints risk management personnel based on its size, significance, and complexity to carry out unit level risk management activities. In addition, the Loan Review Committee and the Investment Review Committee, established under the President, are responsible for managing credit risk and investment risk, respectively.
Furthermore, to incorporate risk management metrics into financial incentive mechanisms, the SCSB has established distinct risk management performance indicators for senior management and general employees, embedding a strong risk management culture into employees’ daily operations.
Three Lines of Defense for Risk Control
Risk Management KPIs Set-up
The SCSB asks managers and employees of the Risk Management Department to set up specific KPIs and job objectives that critically incorporate the risk management metrics into financial incentives. In 2025, the KPIs of the Deputy Executive Vice President of the Risk Management department can be seen in the table below.
| Corresponding ESG Risk | KPIs and Job Objectives in 2023 | Weight(%) |
|---|---|---|
| Market Risk | Conduct Bank‑wide monitoring of trading positions and profit‑and‑loss (P&L). When necessary, notifications are issued to relevant units, and management results are regularly reported to senior management for decision‑making reference. | 4 |
| Operation Risk |
|
14 |
| Credit Risk | In coordination with the deployment of the new e‑loan system for overseas branches, the SCSB established an overseas branch credit rating system and assisted overseas branches in optimizing their rating processes. The system build‑out is expected to be completed in the first quarter, with phased rollout thereafter. | 3 |
| Country Risk | In response to the impact of the U.S. political and economic environment, the SCSB strengthened controls over high‑risk countries, industries, and corporate groups. It conducts regular reviews of relevant financial indicators by country, examines corporate and retail credit portfolios, analyzes problem assets by country, industry, and borrower, and implements dynamic monitoring and early‑warning measures in a timely manner, with records retained for reference. | 3 |
| Climate Risk |
|
11 |
| Others |
|
9 |
Risk Appetite
Risk appetite represents the level and types of risks that the SCSB is willing to accept in the process of achieving its strategic objectives and business plans. Building upon this, the SCSB establishes risk management and quantitative procedures as well as sets both qualitative statements and quantitative limits. The risk appetite and various limits are determined annually based on factors including annual operational targets, statutory capital adequacy ratio requirements for the SCSB and its subsidiaries, financial budgets, business planning, and historical credit utilization rates. These are then submitted to the Risk Management Committee and the Board of Directors for further discussion.
Furthermore, the SCSB reasonably allocates various limits by considering the business portfolios, business scale, and capital scale of each subsidiary to ensure their risk-bearing capacity. The monitoring results are incorporated into risk management execution reports and submitted to the Risk Management Committee and the Board of Directors for quarterly reporting.
| Risk Types | Risk Appetite and Limits | Mitigation Measures and Monitoring Mechanism |
|---|---|---|
| Capital Adequacy |
|
|
| Group-wide Credit Risk |
The SCSB and its subsidiaries’ group-wide credit risk management:
|
|
Risk Assessment of New Products and Services
Before launching new products or services, the review team will conduct a thorough risk assessment and internal inspections to ensure the optimization of risk management and internal control. Apart from identifying the market risk, the credit risk, the operational risk, the liquidity risk, the compliance risk, the climate risk, emerging risks, and other potential factors that might affect business operations, the review team also looks into various aspects including product traits, business strategies, internal control, and customer right protection. Furthermore, prior to launching trust products, it’s pivotal to assess their legitimacy, cost efficiency, risk-return traits, preferred target customers, consistency with the SCSB’s risk management criteria, and market demand. In 2025, 136 cases of both domestic and overseas risk assessments were closed.
Rating Risks by Scale
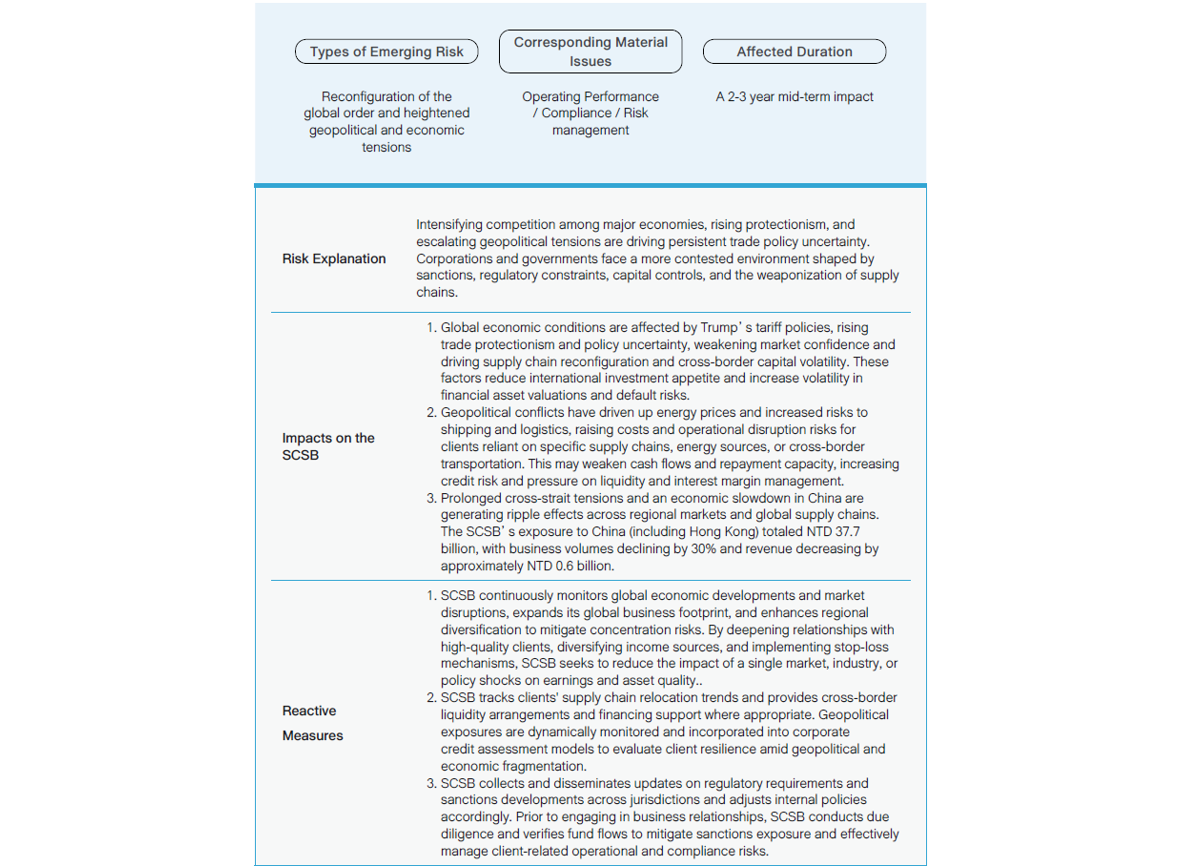
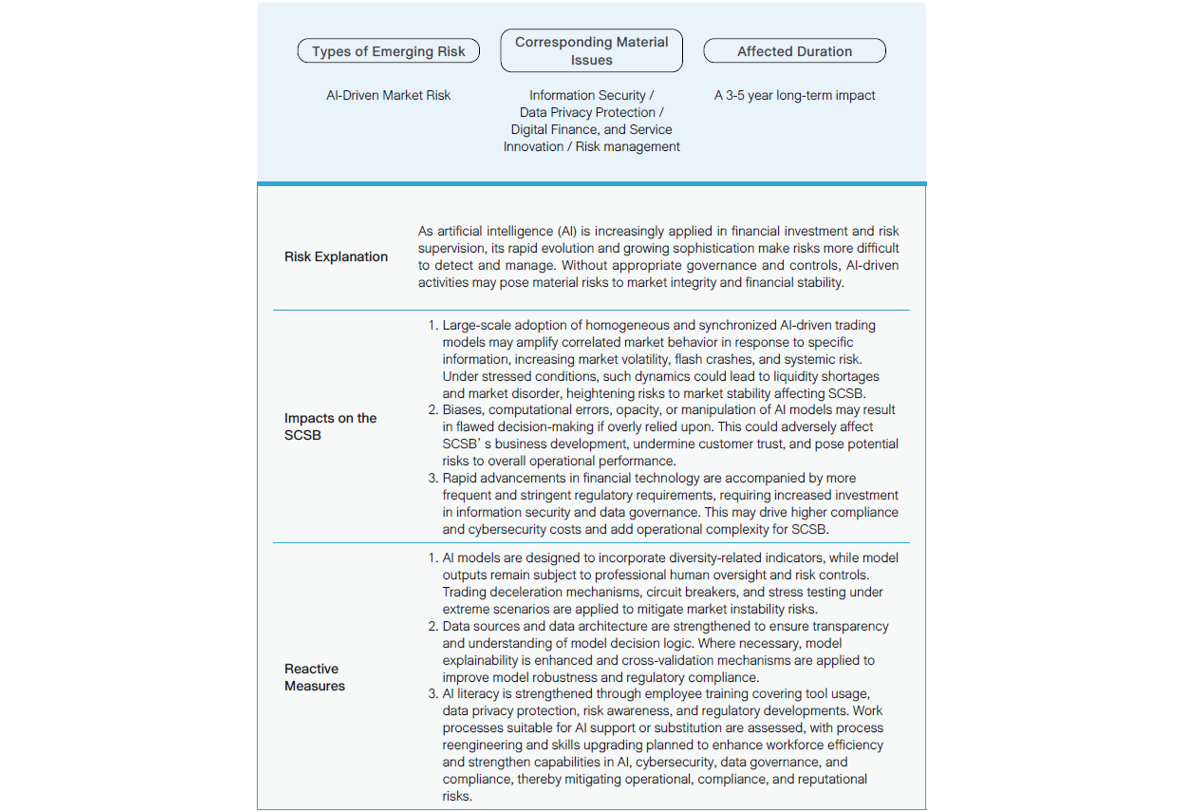
The SCSB incorporates magnitude and likelihood as two important factors into mapping out different risks by scale, where reactive actions and mitigating processes are then developed to cope with risks that could exert prominent impacts on the SCSB. This way, the SCSB is able to reinforce its risk management capability and strengthen the operational resilience consequently.
| Risk Items/ Evaluating Items
(Ranked by risk, with the most significant risks listed at the top) |
Magnitude
(from low to high) (15→ 1) |
Likelihood
(from low to high) (15→ 1) |
Emerging Risk |
|---|---|---|---|
| Uncertainties Stemming from Trump's Economic and Trade Policies | 4 | 2 | |
| Reconfiguration of the Global Order and Heightened Geopolitical and Economic Tensions | 5 | 4 | V |
| Operation Risk-Financial (AI) Scams and Trust Issues | 6 | 6 | |
| AI‑driven Market Risk | 6 | 7 | V |
| Technology Risk | 7 | 7 | |
| The Potential AI Bubble May Lead to Economic Contraction | 7 | 7 | |
| Financial turmoil triggered by the commercial real estate crisis in Europe and the United States | 6 | 10 | |
| Climate Risk | 9 | 8 | |
| Talent Recruitment and Retention | 10 | 7 | |
| Compliance Risk | 8 | 9 | |
| Country Risk (Whole) | 10 | 8 | |
| Credit Risk (Whole) | 9 | 10 | |
| Market Risk (Whole) | 11 | 10 | |
| Operation Risk (Whole) | 11 | 12 | |
| Liquidity Risk | 10 | 14 | |
| Uncertainties Stemming from Trump's Economic and Trade Policies | 4 | 2 |
Information Security
Due to the popularity of digital finance, topics such as personal data protection and information security have received contentious attention within the financial industry in recent years. By acknowledging the importance of information security, the SCSB has acquired the certificate of the ISO 27001: 2022 Information security, cybersecurity and privacy protection- Information security management systems (ISMS) in 2025, set up information security goals, and built up a cross-department information security committee to arrange quarterly meetings and carefully inspect and manage the information security policies, risk assessment, incidents investigation, reports, corrective actions, and regulations.
Structure and Function of Information Security
Information Security Committee
The SCSB's Risk Management Committee is in charge of supervising information security matters, where members of the committee possess rich information security and industry management experience. In addition, Director Chiu Yi-Jen previously served as the CIO of the SCSB, reflecting his expertise in information systems governance and information security management. Likewise, Director Huang Hui-Chu used to serve as General Manager of Taiwan IBM, which pinpoints her profound experience in running the technology industry and advancing digital development. Both of them reflect that board members of the SCSB have relevant experience, industry knowledge, and practices in the information security governance and technological risk management fields.
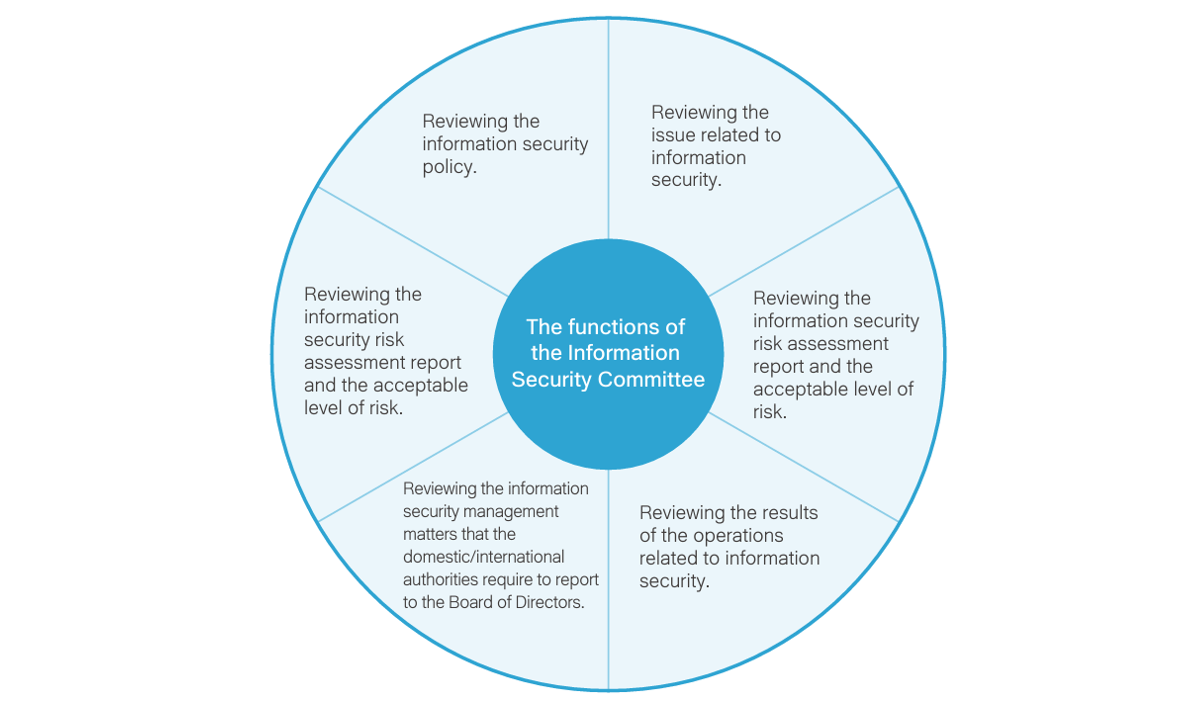
On the other hand, the Information Security Committee under the President is responsible for managing the bank-wide information security. According to Information Security Committee Charter of The Shanghai Commercial & Savings Bank, Ltd., the Committee is set up by seeking approval from executive board members in the first instance. The committee will conduct discussions and oversee matters related to critical business and the information security policy, whilst planning the bank-wide information security measures and their implementation. Lastly, in 2025, the CISO role was set up, and the SCSB‘s Executive Vice President, Lu Shao-Yu, was appointed to serve the position and was in charge of empowering the information security policy and resource allocation.
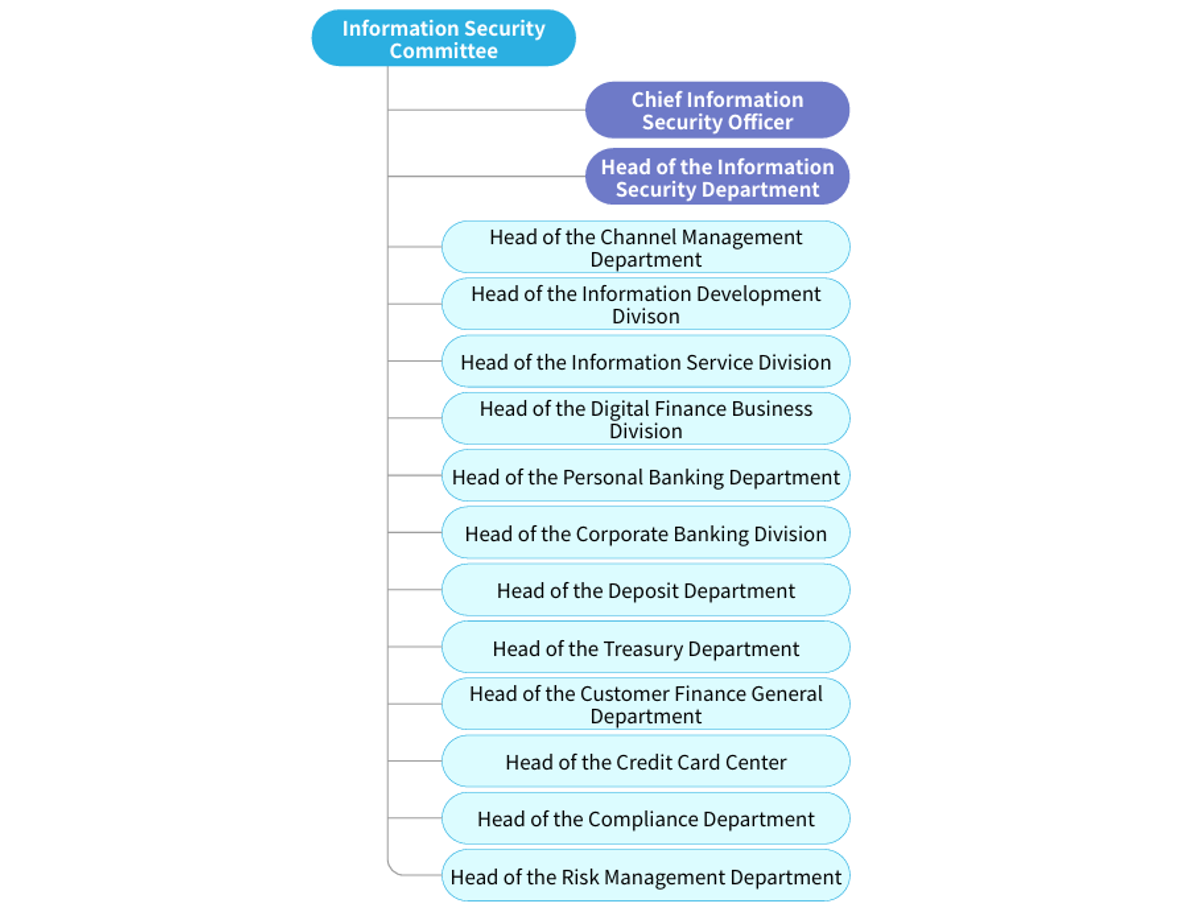
the SCSB states the Risk Management Committee is in charge of supervising information security matters while the Information Security Committee under the President is responsible for managing the bank-wide information security. According to Information Security Committee Charter of The Shanghai Commercial & Savings Bank, Ltd., the Committee is set up by seeking approval from executive board members in the first instance.
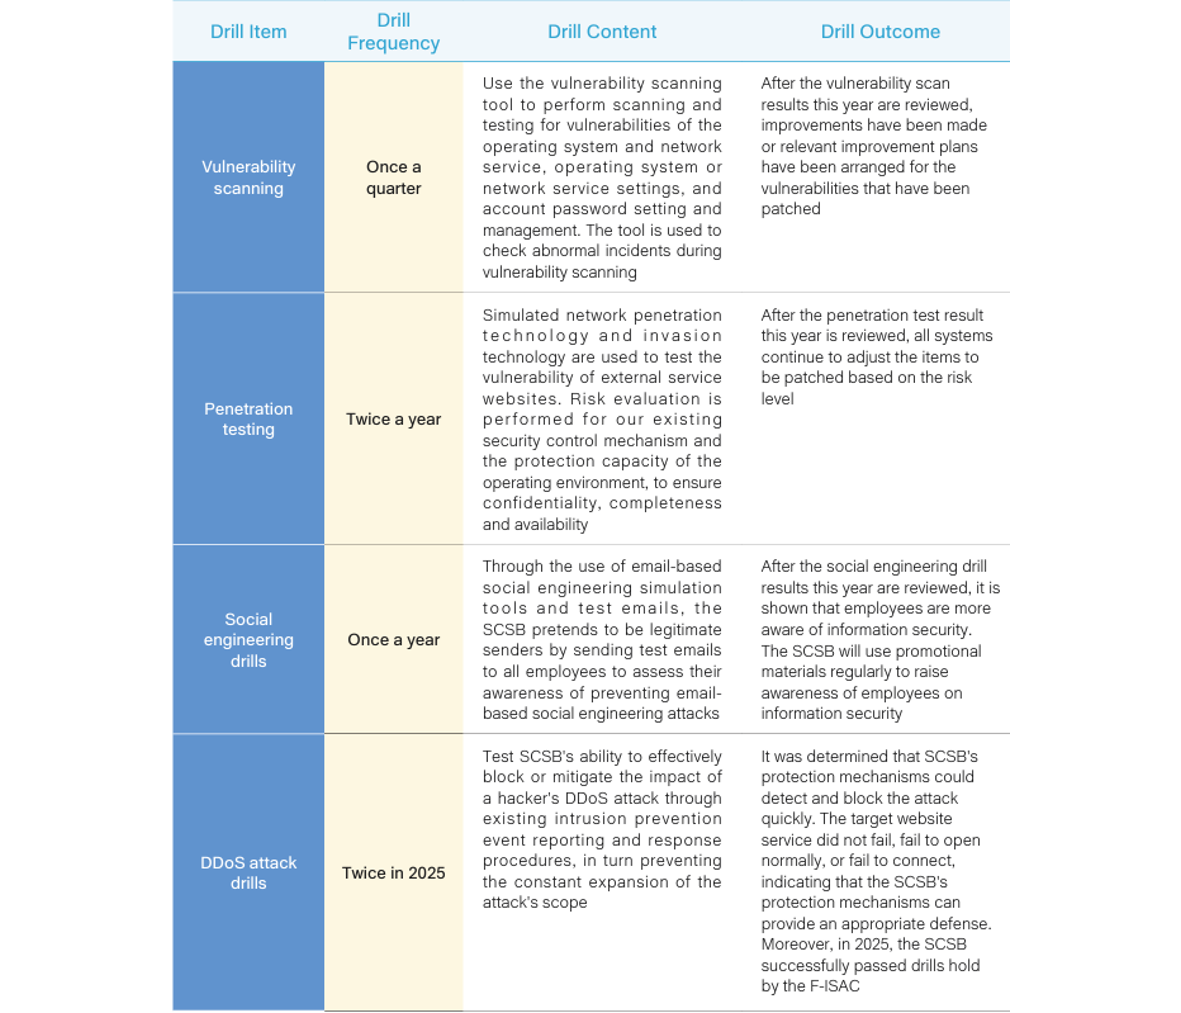
Drill for information security in 2025
3 times of information security drills were held in 2025 (including the social engineering drill and DDoS attack drill) to help all employees become more familiar with real-time actions taken in response to any form of information security incident.
Reinforcement of information security control of IoT
To manage the IoT equipment used for operation management, the SCSB completed the network partition establishment program of IoT equipment. The LAN of the branch is separated by firewalls based on the operating status for easy identification and management. Information security protection of IoT equipment is enhanced. The SCSB continues to strengthen the information security of IoT information systems, raise awareness of correct information security, improve the habit of information security, and avoid information security incidents such as sensitive data exposure.

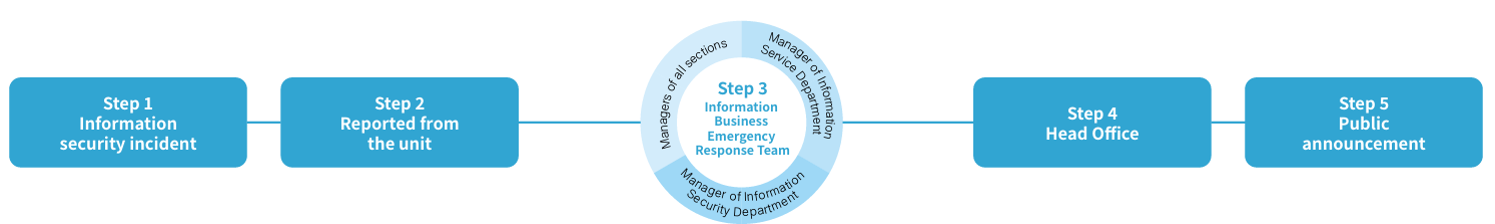
The SCSB explicitly specified the "Regulations Governing Information Security Incidents" and "Establishment Regulations for Information Security Incident Response Team" to define the reporting process and response guidelines for information security incidents. The SCSB is able to resume operation quickly and effectively according to systematic processing procedures and take required improvement measures. When an information security incident occurred, the manager of the Information Service Department,managers of all sections and the manager of the Information Security Department formed the Information Business Emergency Response Team. This team is responsible for taking emergency response measures and activating the continuous operation plan of relevant businesses. Meanwhile, this team helps the Head Office prepare for the press release and explain it to the public. In 2025, there's no detrimental information security-related incident happened in the SCSB.
The reporting procedures for information security incidents
Improve the Customer Service
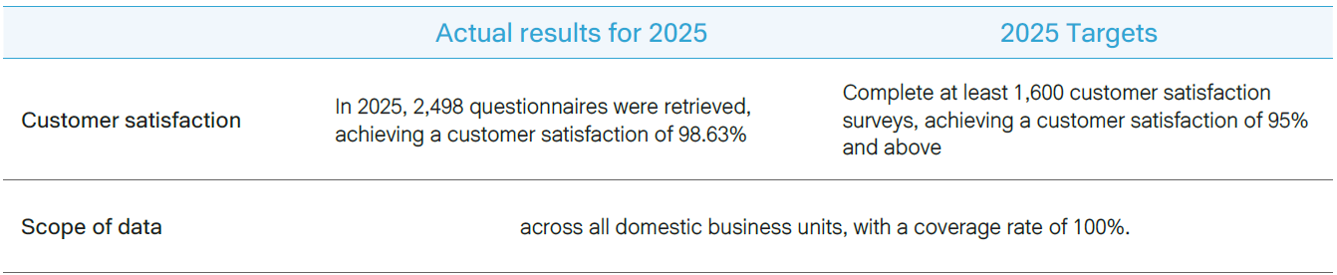
Customer satisfaction survey
Throughout its century-long history, the SCSB has embedded a service-oriented mindset into every aspect of its operations. For example, all new employees are required to complete at least five hours of etiquette training. The SCSB has also developed the “5 Heart to Heart Rules Manual in the Business Hall”, which outlines key service principles across five key customer touchpoints: welcoming, waiting, counter service, transaction, and walking the customer out. Since the launch of service quality evaluations in 2005, the SCSB has consistently demonstrated steady improvement in performance, thanks to the collective efforts of all staff members.
Reporting level of incidents on all levels
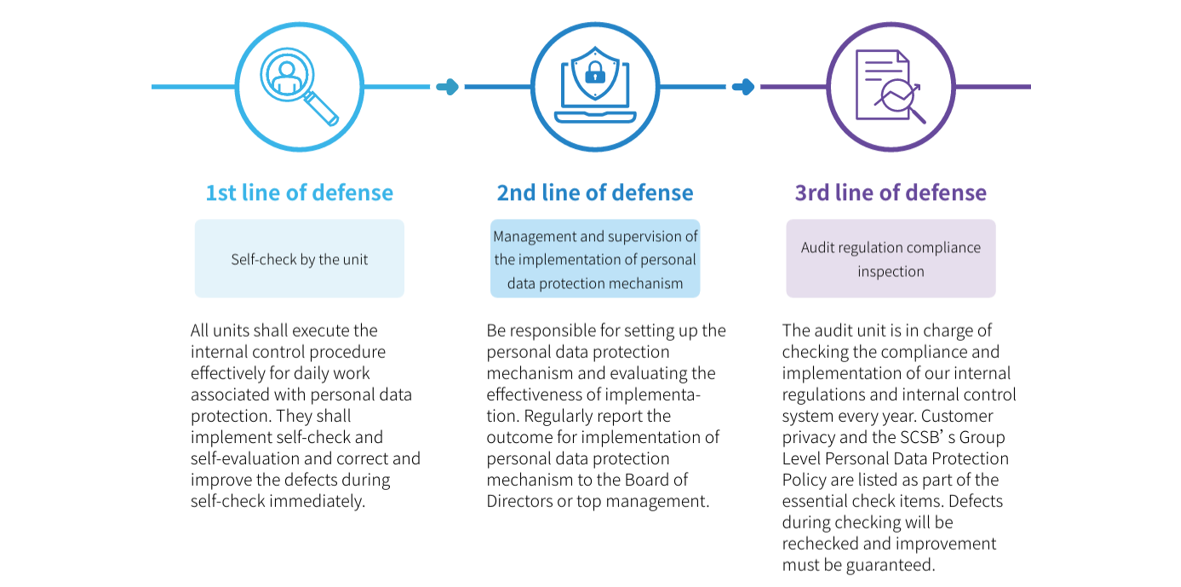
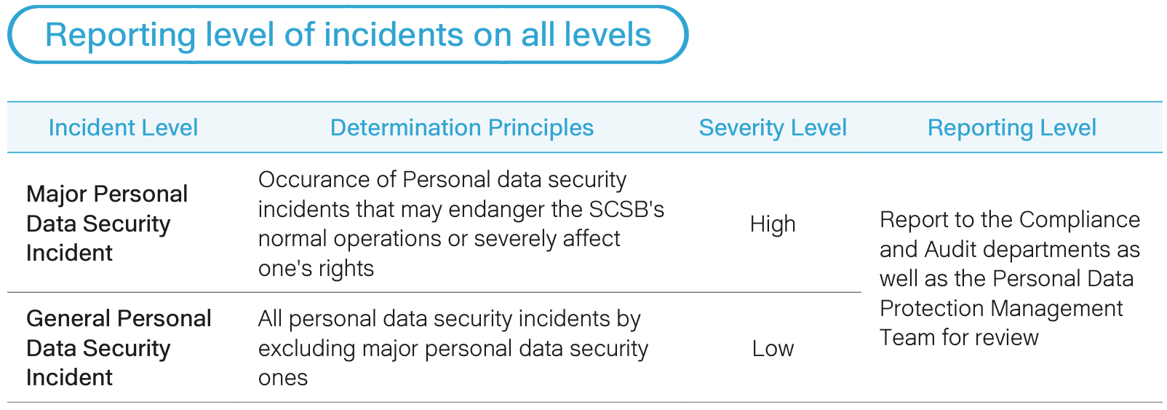
We follow the "Standards Governing the Security of Personal Data Files for the Designated Non-government Agency" established by the Financial Supervisory Commission to establish relative internal regulations for the personal file security maintenance. To prevent personal information from being accessed inappropriately, control measures have been established for the regulations and systems of related operations. These will effectively secure personal information, protect the customer's right to personal information security, and maintain information security and privacy.
The SCSB has paid great attention to the security of personal data protection and adhered to the "Implementation Rules of Internal Audit and Internal Control System of Financial Holding Companies and Banking Industries" since 2017. A certified public accountant (CPA) conducts on-site audits of the design and implementation of the SCSB's personal data management system as well as the compliance of the privacy policy, and the relevant results are submitted annually to the FSC for review and approval.
Customer Rights Notification
To respect the rights of customers to exercise their personal information, the SCSB formulates the “Personal Data Management Policy” to inform customers of the purpose of use of personal information, the type of personal information, the duration, area, target and method of use, the rights and methods in line with the Personal Data Protection Act. Similarly, the subject may exercise his rights in accordance with Article 3 of the Personal Data Protection Act and freely choose to provide his or her personal data when failing to provide impact harnessing the interests of subjects.
The SCSB’s website also clearly states “Notification for the Contents of the Obligation to Inform the Practice” based on Article 8, Paragraph 1 of the “Personal Data Protection Act” with the following key points:
| The type of personal data and information collected | The purpose and use of personal data collected | Protection for the type of personal data collected | Our retention period of collected personal data based on regulations and the purpose of business | The subject and situation of use of personal data by the third-party |
The SCSB fully informs customers of their rights to give prior consent to rights to opt-in and opt-out, request access to data held by the SCSB, and request data correction, deletion, removal of personal data (including transferring personal data to other data service providers), termination of processing and utilizing data accordingly.
The secondary use of customers' personal data refers to telemarketing activities in compliance with the Personal Data Protection Act and other relevant regulations. In 2025, the proportion of customer data subjected to secondary use accounted for 5%. Moreover, internal regulations have been established to govern the above activities and ensure compliance with the following principles :
- Seek customers’ prior written consent or authorization
- Evaluate customers’ ability to maintain the confidentiality of customer data critically before establishing a sound partnership
- Transfer encrypted end-to-end customer data with collaborative partners, and only authorized persons could utilize data for business purposes
- Conduct both regular and spontaneous audits on collaborative partners to examine operations in compliance with legitimacy
The SCSB’s digital development is driven by the vision of offering clients the best digital experience. Focusing on clients’ needs and by applying data analysis, the SCSB strives to provide essential and convenient financial services to its clients. Additionally, it serves as a valuable partner in customer acquisition and retention for the SCSB’s business units and branches. In addition, the SCSB has long been a corporate laboratory member of FinTechSpace and has maintained good interaction with startup companies in the space. Through regular corporate events organized by the space, exchanges between startups and relevant departments of the SCSB can be arranged to explore collaboration opportunities. In 2025, the active online banking users for promotion of digital financial services resulted in a 2.36% increase, an 4.88% increase in active mobile banking users, and a 17.9% growth in digital account openings.
The SCSB has allocated budgets for system development, new feature implementation, and FinTech-related collaboration projects. In conjunction with the centralized application, management and advancement of artificial intelligence (AI) technologies across the bank, the SCSB continues to drive the enhancement, innovation, and development of various digital financial services. Looking ahead to 2026, the SCSB will continue to expand its digital service landscape by actively exploring the adoption of new FinTech technologies and partnerships with startups to develop innovative business models and deliver richer, smarter interactive experiences.
The Main Initiatives Include :
|
1.Personalized new online banking system
To enhance the adoption rate and customer satisfaction of online banking services, the SCSB launched a project in 2022 to develop a brand‑new personalized online banking system. Leveraging new web technologies, the system provides a fully personalized online banking service with user interfaces tailored to individual customer needs. The first phase of service functionalities was officially made available to the public in January 2025, and full rollout was completed in November of the same year. 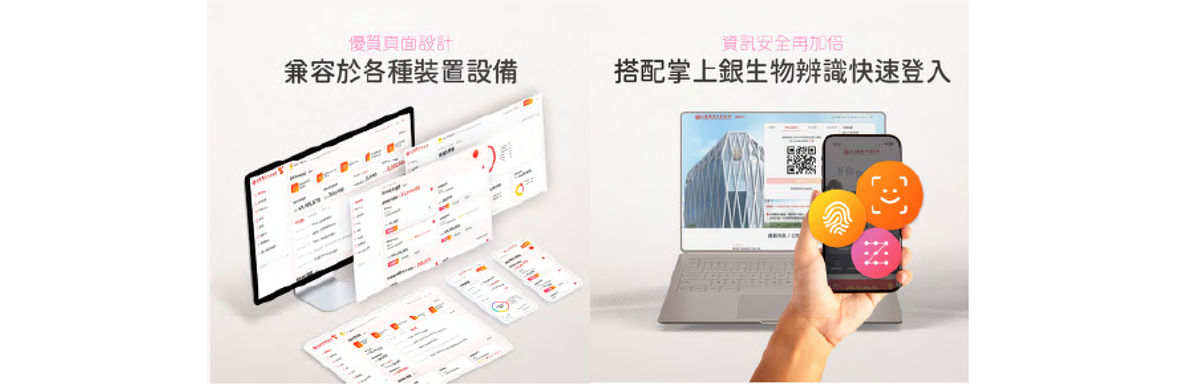
|
|
|
2.Corporate Online Banking App
In October 2025, the Corporate Online Banking App expanded its service scope by adding dozens of transaction and inquiry functions, including foreign currency transfers, remittances and exchanges; small amount TWD transfers; time deposits in both TWD and foreign currencies; online financing and loan repayments; import repayments; and fund investments. Additional features such as password change services, exchange rate target notifications, time deposit pledge loan calculators, push notifications for transaction results, advertising modules, and fast login to the web version were also introduced. These enhancements significantly improve efficiency and value experience for highly mobile users or customers with centralized decision making needs in areas such as transaction execution, password management, and information access, thereby realizing a one stop mobile financial service solution for corporate operations. |
|
|
3.Corporate Online Banking Reconstruction
Our corporate online banking system has been operating steadily for many years. In response to evolving digital transformation requirements and to meet customers’ expectations for intelligent workplace solutions, the SCSB plans to launch a corporate online banking system redevelopment project in the fourth quarter of 2026. This project will focus on enhancing system flexibility and scalability, leveraging technological innovation to help enterprises optimize fund allocation, reduce transaction risks, and improve operational efficiency, with the aim of becoming a preferred partner for corporate cash management. |
|
|
4.LINE Official Account Text Customer Service
The text customer service for corporate customers was launched via the SCSB’s official LINE account in the first quarter of 2025. Powered by SmartRobot, the service provides intelligent and convenient support by presenting frequently asked questions in visualized formats, including infographic cards, step by step process guides, and instructional videos, enabling corporate clients to complete operations efficiently. For more complex operational issues, live text based customer service agents are available to assist clients directly. By integrating robotic automation with human support, the system facilitates human machine collaboration to resolve issues encountered by corporate clients when using the SCSB’s eWB platform and Taiwan Pay merchant services, thereby enhancing overall satisfaction with the digital customer experience. |
|
|
5.Digital Currency Applications
The SCSB took part in the first phase (wholesale) and second phase (universal) retail payment pilot plans of CBDC. For B-end (business) and C-end (consumer), the SCSB designed an application scenario for receipt and payment and cross-border remittance to save time for transactions. As arranged by competent authorities, the SCSB was engaged in the SWIFT CBDC Sandbox Plan. The SCSB works with global institutions participating in this plan, facilitates digital currency exchange among platforms, and builds an international payment ecology. The SCSB will continue to adapt to the plans of competent authorities, pay attention to international development trends, and explore cross-border payment and the application in financial innovation. |
|
|
6. Restructuring of the Digital Banking Department
In response to the quick development of AI and the integration of the utilization, management, and development of AI technology application among the entire bank, the operation of customer experience and data governance and application under the Head Office Strategic Planning Department has been incorporated into the Digital Banking Department in January 2025. |
|
|
7.CloudBank Digital Brand
The SCSB conducted a revision of Cloud Bank, a digital brand website and an existing channel in 2023. Core functions were organized, and information was integrated. The new website was launched in 2024. The young user experience and brand exposure are enhanced via themed activities and gaming interface elements. As of the end of December 2025, the website recorded 67.3 thousands visits and 85.8 thousands information clicks. The DAU/MAU ratio reached 13.5%, indicating that users visited the platform an average of approximately four to five days per month. These reflects improved platform stickiness, with sustained and progressive exposure to the SCSB’s services, thereby laying a solid foundation for the development of future digital business models. 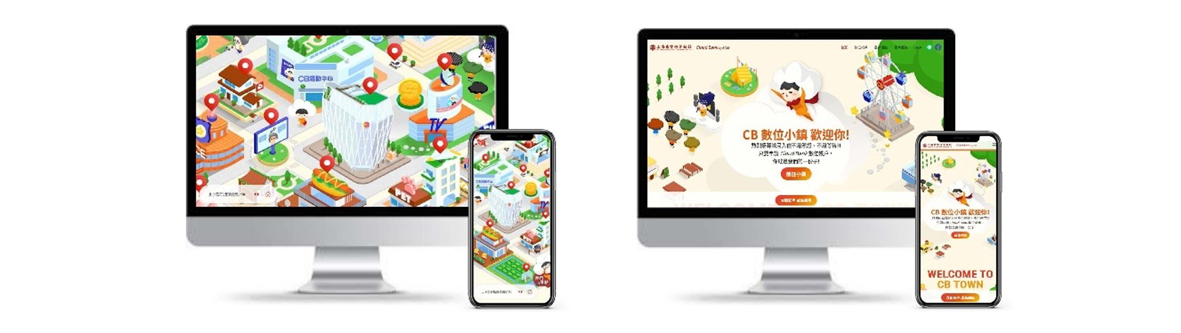
|
|
|
8.LINE Official Account Push Notification Services
The SCSB has expanded its LINE Official Account to include a range of push notification services, such as exchange rate target alerts, incoming fund notifications, and various credit card related notifications. Through timely and diversified push notifications, the SCSB enhances customers’ efficiency in accessing information and overall service experience, further strengthening customer engagement and interaction with the SCSB. |
|